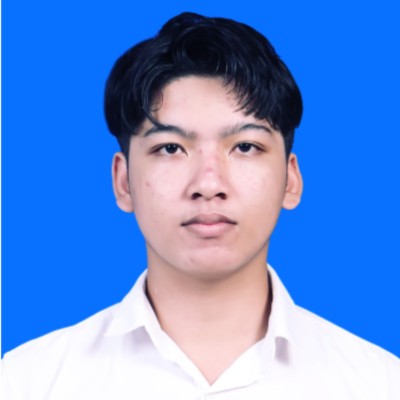
Portrait of Dearen Kansil

Dearen Kansil

Security Research · Open-Source Tooling

Dearen
Kansil

Integrity Verification · Detection · Forensics

I research how systems fail, then I build the tools that catch it. Most of my work starts as offensive research - enumerating, exploiting, understanding what breaks - and ends as a defensive tool anyone can run. Everything I ship is open source, documented, and free.

01 About

research → tooling

I'm an Informatics Engineering student working on offensive security. Most of what I know, I learned by breaking things in labs, CTFs, and on my own infrastructure - enumerating networks, testing web applications, and working through privilege escalation until I understood not just that something failed, but why.

That research turned into tooling. Once I kept re-solving the same problems, I started writing the tools instead - small, focused utilities that anyone can run against their own systems. Everything is open source, because a detection tool nobody can inspect is just another thing you have to trust blindly.

I now work on both sides of that loop: building defensive tools and running assessment support engagements. If you have a specific workflow that needs a tool, or you want to learn offensive security properly rather than from a checklist, get in touch.

How I work

  1. 01 Research — find what actually breaks
  2. 02 Build — write the tool that catches it
  3. 03 Document — open source, free to use

02 Tools & Projects

free · open source · self-hosted

T-01

ReCheck-Integrity

Stable

A Python CLI tool for generating and verifying file and directory integrity using cryptographic hashes, with baseline manifests and recursive verification.

Use case Establish a known-good baseline, then prove whether anything on a host changed since. Useful for forensics, compliance checks, and incident response triage.

  • SHA-256 and MD5 hash algorithms
  • Baseline manifest generation
  • Recursive directory verification
  • Verification reporting
  • Python
  • Cybersecurity
  • Tools
  • Cryptography

2026 · Stable

T-02

Next tool

Planned

In active research. Each tool here started as a problem I hit repeatedly during assessment work, so this one will too — details land when it's usable.

- · Planned

T-03

Next tool

Planned

In active research. Each tool here started as a problem I hit repeatedly during assessment work, so this one will too — details land when it's usable.

- · Planned

T-04

Next tool

Planned

In active research. Each tool here started as a problem I hit repeatedly during assessment work, so this one will too — details land when it's usable.

- · Planned

T-05

Next tool

Planned

In active research. Each tool here started as a problem I hit repeatedly during assessment work, so this one will too — details land when it's usable.

- · Planned

03 Services

custom work alongside open source

S-01

Custom security tooling

A small, focused utility built around your actual workflow - not a repackaged framework. Scoped tight, documented, and handed over as a repo you own.

You get
Repository, documentation, and a handover session
Typical scope
Single-purpose CLI or script, agreed before work starts
Request

S-02

Assessment support

Scoped web application and network testing with written findings. Useful when you need a second set of eyes on an engagement or want findings you can hand to a team.

You get
Documented findings with reproduction steps and remediation notes
Typical scope
Junior to mid-level scope, defined and agreed in writing first
Request

S-03

Training & mentoring

Hands-on sessions built from real labs and CTFs, focused on understanding the reasoning behind each step rather than memorising a checklist.

You get
Lab walkthroughs, practice material, and room for your own questions
Typical scope
One-on-one or small group, beginner to intermediate
Request
  1. Briefyou describe the problem
  2. Scopeagreed in writing
  3. Buildwork, with updates
  4. Handoverrepo, docs, walkthrough

04 Certificates

click a card to view it full

05 Contact

Accepting custom tool requests

email

Tell me what you're trying to do and what's getting in the way. If I can build it, I'll tell you what it takes; if I can't, I'll say so rather than waste your time.